

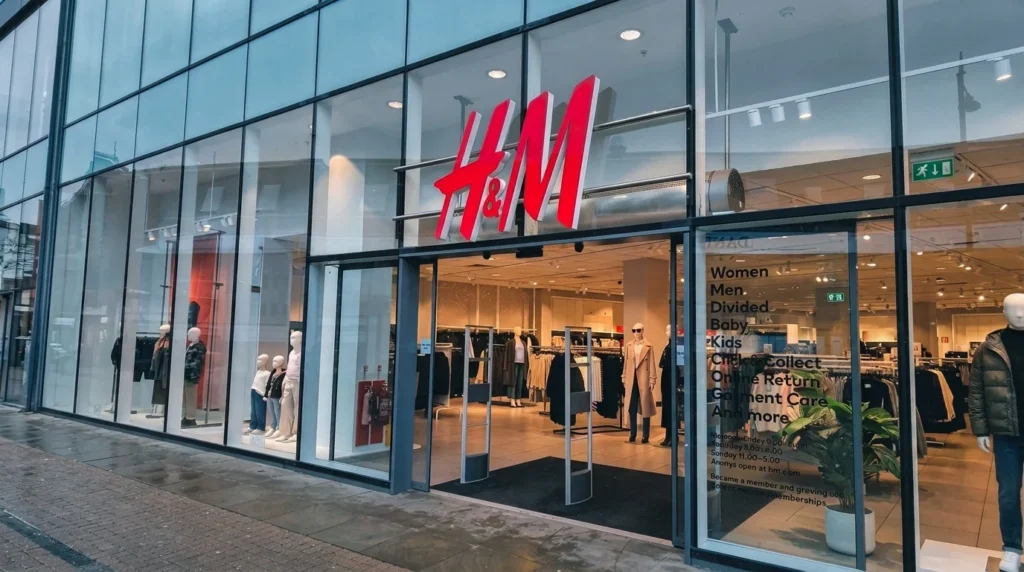
Executive Summary
The H&M data breach claim under investigation by H&M Group now points to GreyOrange, an Atlanta-based supplier of warehouse and store inventory software. The Times first reported the claim on 12 October 2026 and named the ShinyHunters group. H&M said the same day it had found no indication that its data environment was compromised. On 14 October Cybernews reported that an extortion group had given H&M three days to make contact before data is leaked. The sample files the group shared traced back to GreyOrange software. Neither company has confirmed a breach and no customer or employee data has been shown to be involved.
H&M Data Breach Samples Lead to a Warehouse Platform
Cybernews researchers examined JSON records the group posted on Telegram and found product image URLs and identifiers that could be attributed to H&M. They linked the records to GreyOrange. BankInfoSecurity said the sample appeared tied to GreyOrange’s robotic fulfilment systems and included order information with links to garment images on hm.com.
The records don’t show that the attackers hold “more sensitive info, such as personal employee data”, they said. It depends on how GreyOrange connects to a customer’s systems.
The supplier has documented its own reach inside H&M. In a 1 September 2026 announcement, GreyOrange said H&M Group rolled out its GreyMatter software at a West Coast distribution centre in 2021. GreyMatter is the orchestration layer that directs robots and order picking inside a warehouse. The deployment has since spread to other North American sites, while GreyOrange’s gStore inventory app runs in hundreds of H&M stores on three continents. BankInfoSecurity dates H&M’s use of the robots to 2022; the supplier’s own account says 2021.
The Group Behind the Ultimatum Is Unclear
The Times tied the claim to ShinyHunters. When Cybernews checked the listing that carried that name, the ShinyHunters account was marked as retired and the server where the group keeps its datasets held nothing on H&M. Its researchers suggested this could be “random hackers claim to be ShinyHunters”.
On 13 October a collective calling itself ShinyEquationCartel said on Telegram and a darknet site that it was responsible, BankInfoSecurity reported. It claims to include former members of ShinyHunters, Lapsus$, HellCat and LockBit. Swedish newswire Finwire, citing The Times, reported that H&M may have been targeted by the group behind the ASOS attack, which calls itself Xuanye.
None of these attributions has been independently confirmed.
H&M’s Response and the GDPR Clock
H&M’s answer on the data breach claim hasn’t changed. To The Times it described the claims as concerning “a limited scope of H&M Group data”. To TT its press office wrote that it had so far seen no indications of a breach. A spokesperson told ISMG on 13 October, “At this time, we have not found any indications that our data environment has been compromised.” The share was down about 1.4% in Stockholm that afternoon after a steeper early fall, Finwire reported.
If personal data is involved, the GDPR requires notification to the supervisory authority within 72 hours of the company becoming aware. For Stockholm-based H&M that is IMY (Integritetsskyddsmyndigheten). The UK’s ICO had received no report as of lunchtime on 12 October, The Times reported. H&M has faced a data protection regulator before, in October 2020 the Hamburg commissioner fined it €35.3 million over employee profiling at its Nuremberg service centre which came to light when a configuration error exposed the data company-wide.
No Word Yet From GreyOrange
As of 16 October, no outlet in our coverage sweep had reported a GreyOrange statement or a leak of the data. The three-day window Cybernews reported on 14 October runs to about 17 October. It isn’t known whether the files came from H&M’s deployment or another GreyOrange customer, how many records exist or who posted the deadline.
H&M’s Denial Covers Its Own Environment
Every H&M statement on the H&M data breach claim refers to its own data environment. The samples point somewhere else, a platform GreyOrange runs inside H&M warehouses and stores. Both can be accurate at once which leaves the supplier as the party that can settle the claim. Six weeks ago GreyOrange credited H&M for helping it reach 3,800 live stores. As of 16 October it had not said whether its own systems were accessed.
References
- H&M Group announces GreyOrange as a warehouse automation partner
- Hamburg Commissioner Fines H&M 35.3 Million Euro for Data Protection Violations in Service Centre
- H&M faces data leak threat as suspected breach trail leads to warehouse supplier
- Retailers TFG London and H&M Probe Potential Data Breaches
- H&M avfärdar misstankar om hackerintrång
- H&M utreder möjlig cyberattack
This post is also available in:
 Svenska
Related News
Denmark CPR Breach: 8.8 Million Records Pulled via Pays ApS
The Denmark CPR breach exposed the names, addresses and CPR numbers of about 8.8 million people after unknown users abused the legal lookup access of…
 October 13, 2026
Polish Medyc Breach Exposes Patient IDs After SQL Injection Went Unnoticed
September 29, 2026 
Dustin Takes Orders by Phone, Cannot Yet Say What Attackers Reached
September 8, 2026